NIST CSF 2.0 Overview: The 6 Functions, Tiers, and Profiles
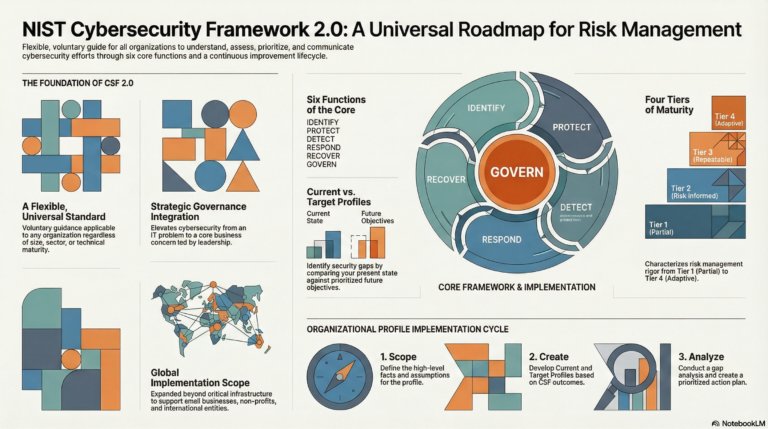
The NIST Cybersecurity Framework (CSF) 2.0 is a voluntary framework for managing cybersecurity risk. NIST released it in February 2024, the first major update since the framework launched in 2014, and the big headline was simple: there are now six functions instead of five, and the new one, Govern, belongs to leadership.
This page is the reference version: what’s in the framework and how the pieces fit. If you want the “how do we actually start” version, read our practical NIST CSF guide.
The Three Parts of CSF 2.0
- The Core: the outcomes you want, organized into 6 functions, 22 categories, and 106 subcategories.
- Organizational Profiles: a snapshot of where you are today (Current Profile) and where you want to be (Target Profile).
- Tiers: a four-level scale for how rigorous your cyber risk governance and management are.
Most people only learn the functions. That’s fine for a first conversation, but Profiles are where the framework becomes a plan, and Tiers are how you explain maturity to a board.
The Six Functions at a Glance
| Function | Code | Categories | Subcategories | What it covers |
|---|---|---|---|---|
| Govern (new) | GV | 6 | 31 | Strategy, risk appetite, roles, policy, oversight, supply chain risk |
| Identify | ID | 3 | 21 | Assets, risk assessment, improvement |
| Protect | PR | 5 | 22 | Identity and access, awareness training, data security, platform security, resilience |
| Detect | DE | 2 | 11 | Continuous monitoring and analyzing adverse events |
| Respond | RS | 4 | 13 | Incident management, analysis, reporting, and mitigation |
| Recover | RC | 2 | 8 | Restoring operations and communicating during recovery |
The functions aren’t steps you finish in order. They run at the same time. You don’t complete Identify and then move on to Protect.
What Govern Adds
Govern pulls together the leadership side of security that used to be scattered across the framework. Its six categories are Organizational Context (GV.OC), Risk Management Strategy (GV.RM), Roles, Responsibilities, and Authorities (GV.RR), Policy (GV.PO), Oversight (GV.OV), and Cybersecurity Supply Chain Risk Management (GV.SC).
My take: Govern is the reason to revisit your program even if you were “done” with CSF 1.1. Most organizations had decent technical controls and weak answers to “who decided this risk was acceptable?”
Implementation Tiers
| Tier | Name | What it looks like |
|---|---|---|
| 1 | Partial | Ad hoc and reactive. Little awareness of cyber risk at the organizational level. |
| 2 | Risk Informed | Management is aware of risks, but practices aren’t consistent across the organization. |
| 3 | Repeatable | Formal, approved policies applied consistently and updated as things change. |
| 4 | Adaptive | Practices adapt continuously based on lessons learned and changing threats. |
Tiers aren’t a grade you must max out. Tier 4 everywhere is expensive and usually unnecessary. Pick the tier that matches your risk.
Organizational Profiles
A Current Profile describes the outcomes you achieve today. A Target Profile describes the outcomes you want, given your risks and priorities. The gap between them becomes your roadmap and budget request. CSF 2.0 also introduced Community Profiles, which are shared baselines built for a specific sector or use case.
What Changed From CSF 1.1
- Scope expanded from critical infrastructure to organizations of every size and sector.
- Govern was added as a sixth function.
- Categories went from 23 to 22 and subcategories from 108 to 106 as overlapping outcomes were merged.
- NIST added Quick Start Guides and implementation examples to make it easier to use.
Free Official Resources
Everything you need from NIST is free. Start with the NIST CSF website, which links to the full CSF 2.0 document, the Quick Start Guides (including one for small businesses), and the CSF 2.0 Reference Tool for browsing every subcategory.
FAQ
What is NIST CSF 2.0?
The 2024 version of NIST’s voluntary Cybersecurity Framework. It organizes cybersecurity outcomes into six functions and adds Govern, which focuses on strategy, oversight, and accountability.
How many functions are in NIST CSF 2.0?
Six: Govern, Identify, Protect, Detect, Respond, and Recover.
How many categories and subcategories does CSF 2.0 have?
22 categories and 106 subcategories, down from 23 and 108 in version 1.1.
What are the NIST CSF tiers?
Partial (Tier 1), Risk Informed (Tier 2), Repeatable (Tier 3), and Adaptive (Tier 4). They describe how rigorous your cyber risk governance and management are.
Is NIST CSF a certification?
No. There’s no official NIST CSF certification for organizations. Companies can be assessed against it, but certifiable standards like ISO/IEC 27001 work differently.
3 Comments