ISO 27001 vs SOC 2: The Difference Explained for Busy Leaders
A big prospect sends over a security questionnaire, and somewhere on page two it asks: “Do you have a SOC 2 report or ISO 27001 certification?” If you’ve never pursued either, this is where the scramble starts.
They overlap a lot, but they’re not the same thing, and the right first choice usually depends on who your customers are.
What Each One Is
ISO/IEC 27001 is an international standard. You build an information security management system, an accredited certification body audits it, and you get a certificate that’s valid for three years with yearly surveillance audits.
SOC 2 is an attestation report from the American Institute of CPAs (AICPA) framework. A licensed CPA firm examines your controls against the Trust Services Criteria (security, availability, processing integrity, confidentiality, and privacy) and writes a report. There’s no certificate. You share the report with customers, usually under NDA.
Side by Side
| ISO 27001 | SOC 2 | |
|---|---|---|
| Output | Public certificate | Private audit report |
| Who audits | Accredited certification body | Licensed CPA firm |
| Where it’s expected | Global, especially Europe and Asia | Mainly North America, especially SaaS |
| Scope | Your whole ISMS (you define the boundaries) | The systems and criteria you choose |
| Types | One certification | Type I (design at a point in time) or Type II (operating over a period, often 3 to 12 months) |
Which Should You Do First?
If most of your customers are U.S. companies buying software or cloud services, SOC 2 Type II is usually what their security teams want to see. If you sell internationally, or into industries that think in ISO terms, ISO 27001 often carries more weight.
Honestly, the deciding factor is your sales pipeline. Look at the last ten security questionnaires you received. Whichever one shows up more is your answer.
Can You Do Both?
Yes, and many growing companies eventually do. The controls overlap heavily, so evidence gathered for one does a lot of the work for the other. Compliance automation tools can collect that evidence once and map it to both frameworks.
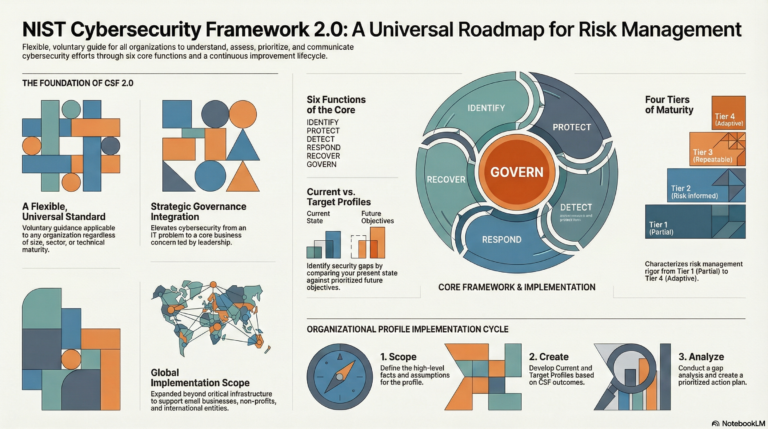
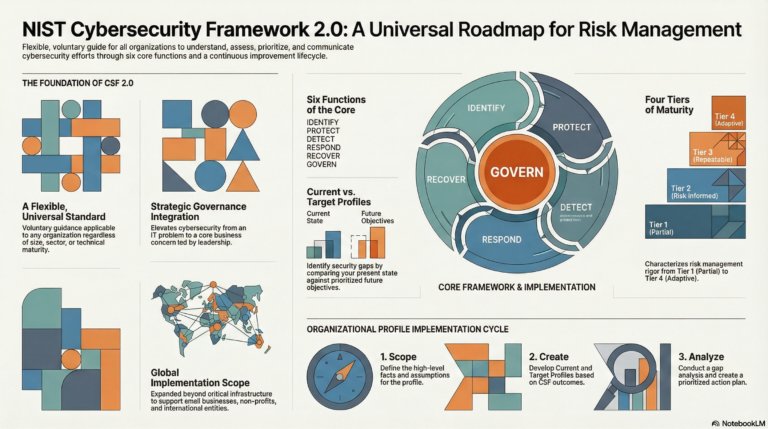
If you’re building your program from scratch, the NIST CSF 2.0 structure is a good way to organize it so either audit is easier later.
FAQ
Is SOC 2 a certification?
No. SOC 2 is an attestation report written by a CPA firm. ISO 27001 is a certification.
What is the difference between SOC 2 Type I and Type II?
Type I checks whether controls are designed properly at a single point in time. Type II checks whether they actually operated effectively over a period, usually several months.
Does ISO 27001 replace SOC 2?
Not always. Some U.S. customers specifically ask for a SOC 2 report even if you hold ISO 27001. Check what your buyers require.
How long does SOC 2 take?
A Type I can be done in a few months if your controls are ready. A Type II adds an observation period, commonly three to twelve months.